AI privacy is not declared.
It is controlled.
The Nexnetic AI Privacy Center makes the models, data, transfers, controls and evidence of your AI installation visible. It separates what the system can verify automatically from what your organization must decide and document.
The Privacy Center is a governance and technical verification tool. It does not replace the assessment of privacy or legal advisors, and it is not a certification of compliance.
Do you really know what your AI is doing?
Models
Which models are authorized, which are configured and which model actually produced each answer from your AI system.
Data
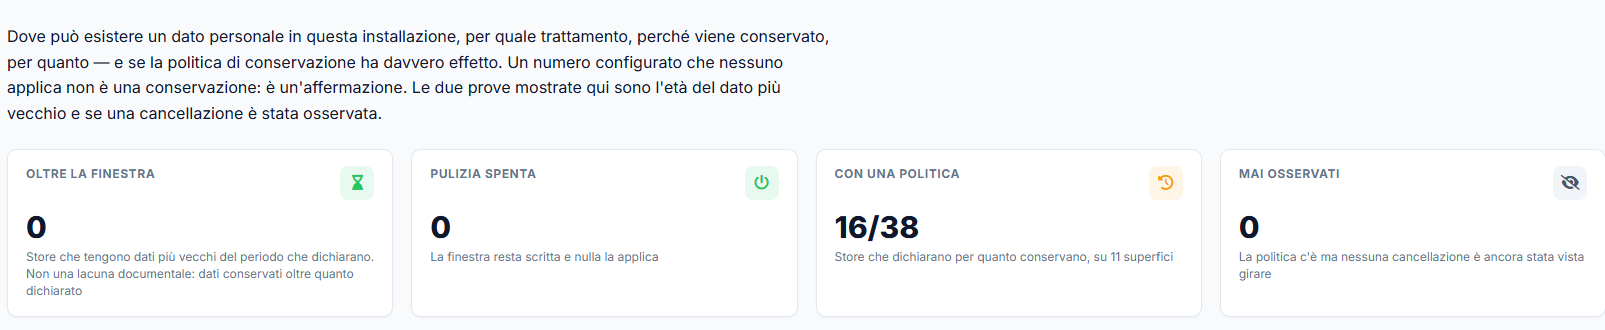
Where personal data may be present, where it is stored and which retention policies are configured.
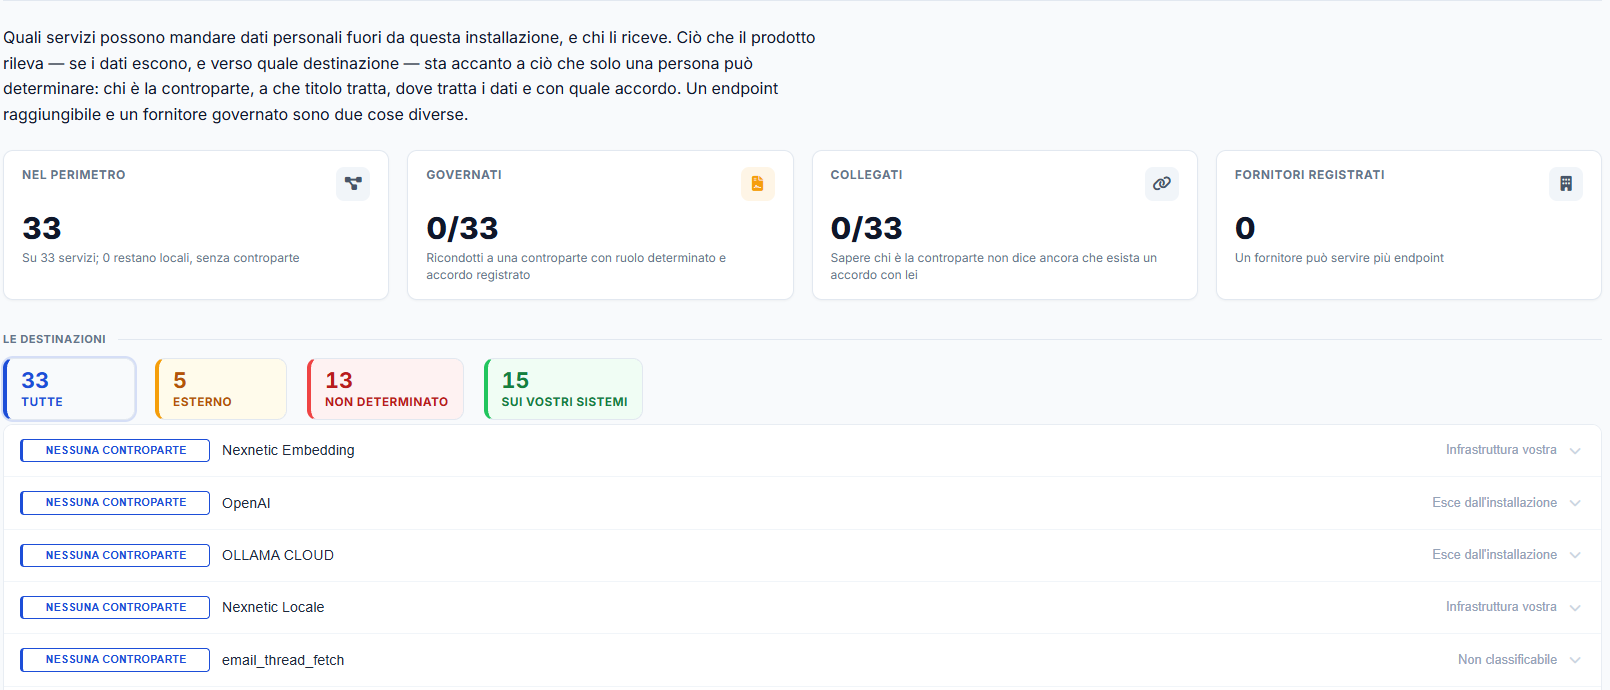
Providers and transfers
Which services stay on your infrastructure and which may involve communication with external systems.
Controls and evidence
Human supervision, technical controls, anomalies, audits and documentary evidence to support governance.
Configuration declared ≠ actual behavior
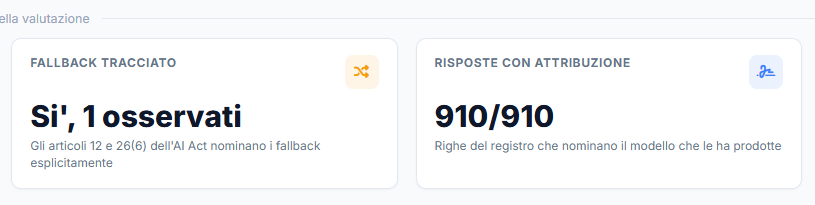
In the observed window: 910 out of 910 answers attributed to the model that produced them.
The Privacy Center also records any model fallbacks.
Nexnetic AI does not just record how the system should behave. Where technically possible, it collects evidence of what actually happened.
Your personal data stays under control
The Privacy Center shows where personal data is processed, which retention policies are active and how technical measures (encryption, anonymization, access control) limit their visibility. It makes verifiable, rather than merely declared, how your policies are respected.
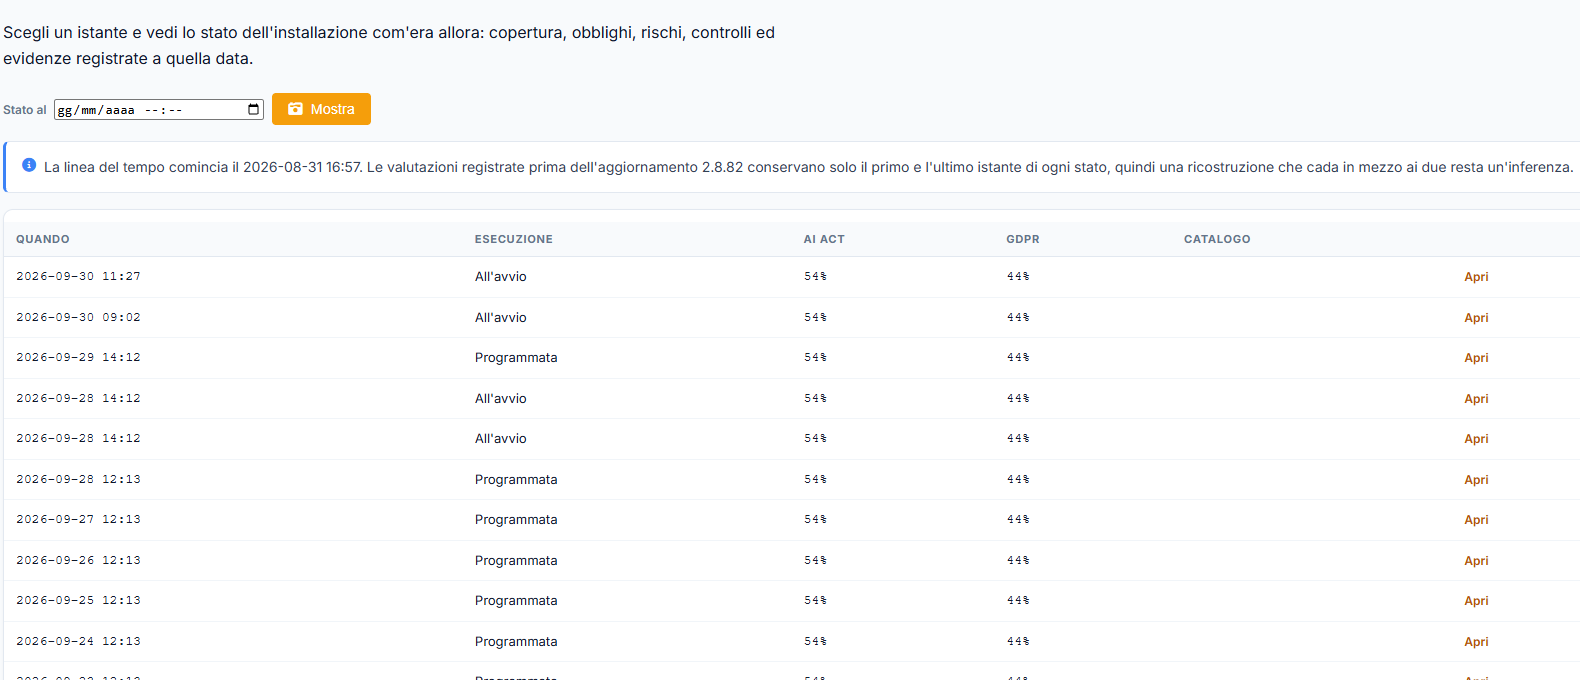
A snapshot of conformance over time
Conformance is not a state to be captured once. The Privacy Center keeps the history of assessments to reconstruct how configuration, controls and evidence have changed over time.
Each assessment preserves the state of controls, obligations and evidence available at that time.
From configuration to evidence
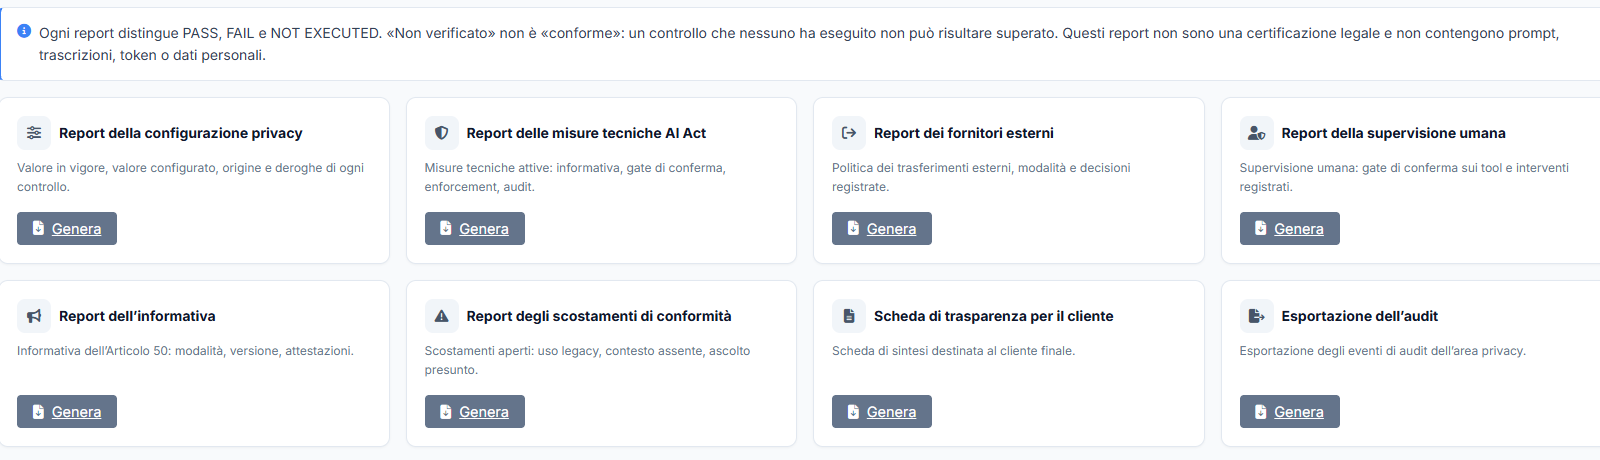
The Privacy Center produces reports and exports that turn configurations, controls and audits into verifiable documentation.
- Privacy configuration report
- AI Act technical measures
- External provider inventory
- Human supervision
- Privacy notice
- Detected deviations
- Transparency sheet
- Audit